

Stop Guessing Who Has Access to What in AWS
If you’ve ever looked at your AWS environment and thought, “I have no idea if these permissions are too broad,” you’re not alone. Most teams give out IAM permissions quickly and rarely go back to clean them up. Over time, that adds up to a serious problem.
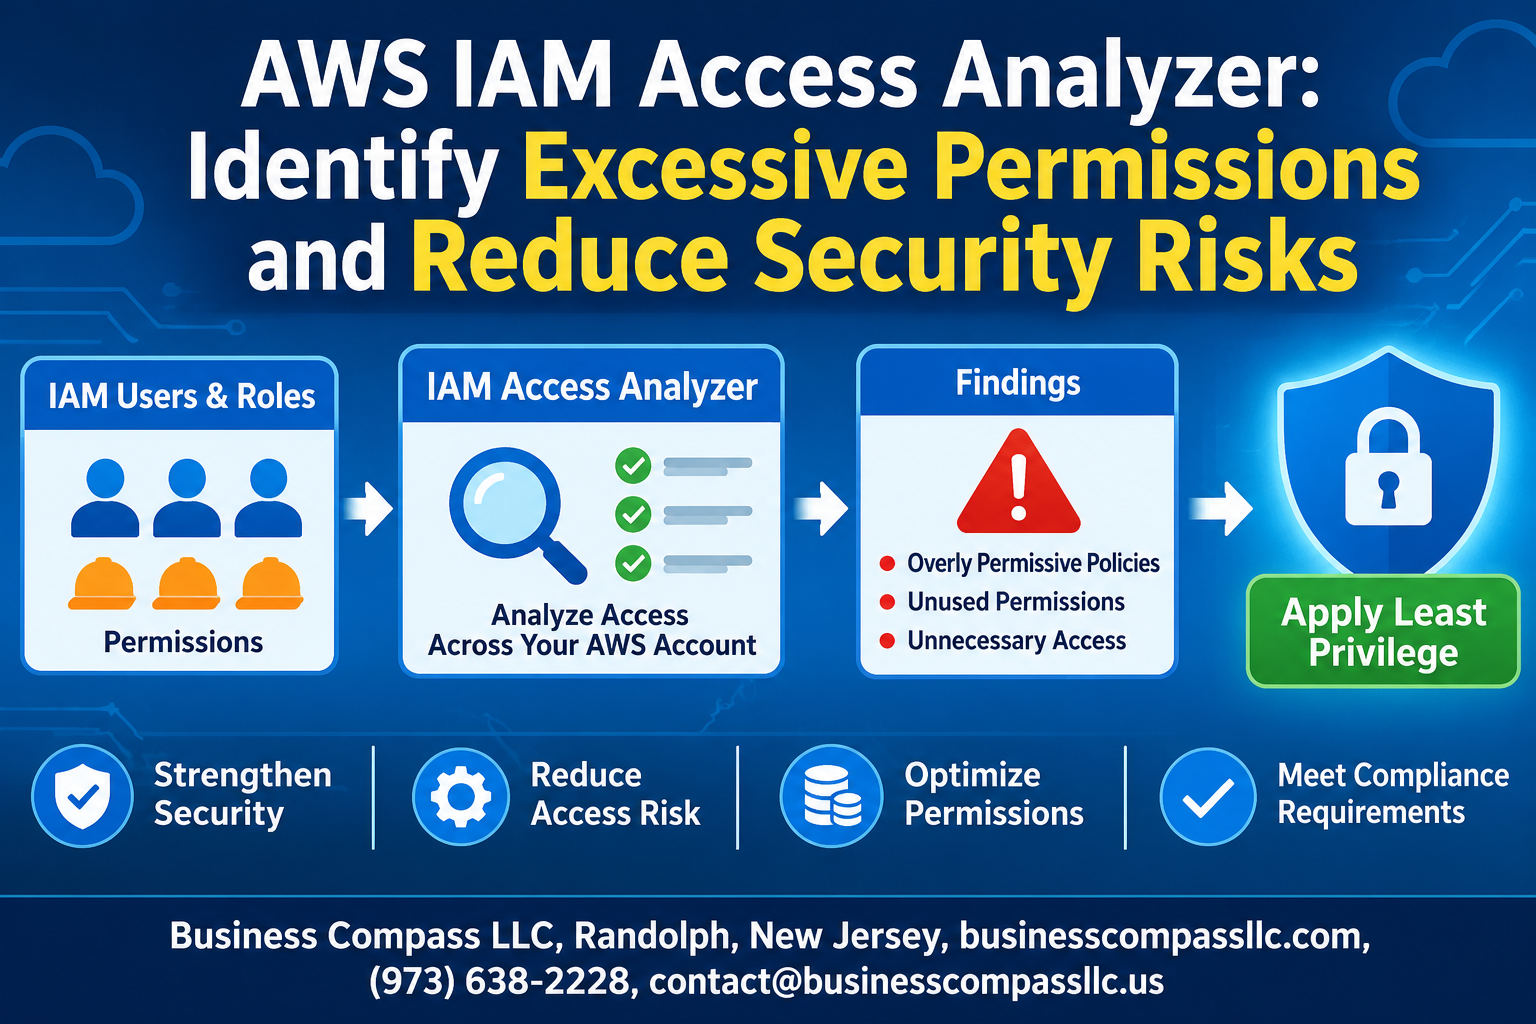
AWS IAM Access Analyzer is built to fix exactly that. It scans your environment, spots excessive IAM permissions, and flags resources that are exposed to more access than they should be — before that exposure turns into a breach.
This guide is for AWS engineers, security teams, and cloud architects who want to tighten up access control without spending weeks auditing policies by hand.
Here’s what you’ll walk away with:
- How Access Analyzer actually works and why it belongs in your AWS security best practices toolkit
- How to set it up and read its findings so you’re not just collecting alerts but actually acting on them
- How to automate continuous permission monitoring so your AWS environment stays clean as it grows — not just right after a cleanup sprint
No fluff, no theory — just a practical breakdown of how to get from “I think our permissions are fine” to “I know exactly who can access what and why.”
Understanding AWS IAM Access Analyzer and Its Purpose
What AWS IAM Access Analyzer Does for Your Security Posture
AWS IAM Access Analyzer scans your policies to flag resources shared externally, helping you catch excessive IAM permissions before attackers do. It supports AWS least privilege access by continuously analyzing resource policies across S3, IAM roles, KMS, and more—giving you clear, actionable findings without manual digging.
Identifying Excessive Permissions Across Your AWS Environment
Detecting Overly Permissive Policies in Real Time
AWS IAM Access Analyzer continuously scans policies, flagging excessive IAM permissions before they become breaches.
Recognizing Cross-Account and External Access Risks
It catches unintended external access across accounts instantly.
Spotting Unused Permissions
Unused permissions silently expand your attack surface.
Analyzing Resource-Based Policies
Hidden vulnerabilities in resource policies get exposed automatically.
Setting Up AWS IAM Access Analyzer for Maximum Coverage
Enabling Access Analyzer at the Organization or Account Level
Enable AWS IAM Access Analyzer through the IAM console, selecting organization-level for full coverage across all accounts.
Defining Analyzer Scope to Match Your Security Requirements
- Set trusted zones to match your AWS environment boundaries
Integrating Access Analyzer With AWS Security Hub for Centralized Visibility
Connect both services to consolidate excessive IAM permissions findings centrally.
Interpreting and Acting on Access Analyzer Findings
Understanding Finding Types and Severity Levels
AWS IAM Access Analyzer flags external access, unused access, and policy validation findings. Prioritize high-severity external-access findings first — these signal real exposure. Archive resolved or accepted risks to keep your baseline clean. Use filters targeting specific resources or principals to cut through noise and track remediation progress consistently.
Reducing Security Risks Through Policy Optimization
Applying Least Privilege Principles Based on Analyzer Insights
AWS IAM Access Analyzer flags overly broad permissions, helping you trim access to only what’s needed. Use findings to replace wildcard actions with specific ones.
Generating Policy Recommendations to Tighten Access Controls
- Use IAM policy generation based on CloudTrail activity
Validating Updated Policies Before Deploying Them
- Run policy validation checks before pushing changes
Automating Continuous Permission Monitoring at Scale
Setting Up CloudWatch Alerts for New Access Analyzer Findings
Configure CloudWatch Events to trigger alerts whenever Access Analyzer flags new findings, keeping your team instantly notified.
Automating Remediation Workflows With AWS Lambda
- Wire Lambda functions to auto-revoke excessive IAM permissions
- Run policy cleanup scripts on every new finding
Scheduling Regular Access Reviews
Catch permission drift early with weekly automated scans.
AWS IAM Access Analyzer is a powerful tool that takes the guesswork out of managing permissions across your AWS environment. From spotting excessive access and interpreting findings to optimizing policies and automating monitoring at scale, it gives you a clear picture of who can access what — and helps you lock things down before small gaps turn into big problems.
The best part? You don’t have to do this all at once. Start by setting up Access Analyzer with proper coverage, tackle the highest-risk findings first, and gradually build automation into your workflow. The tighter your permissions, the smaller your attack surface — and that’s a win for your entire organization. Start reviewing your Access Analyzer findings today and take the first step toward a more secure AWS environment.