

AWS Secrets Manager and Kubernetes ESO Integration: A Step-by-Step Implementation Guide
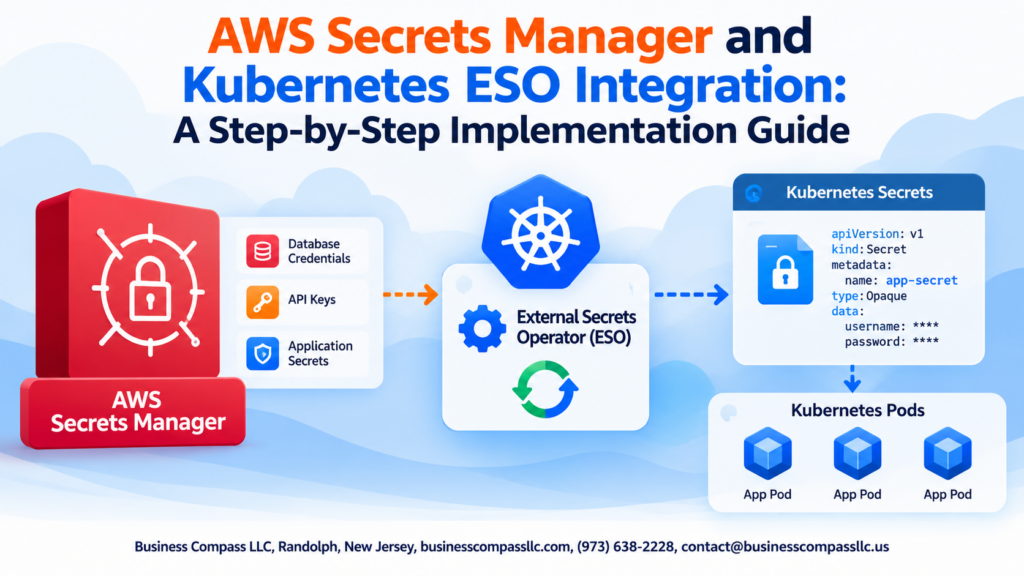
Stop Hardcoding Secrets in Your Kubernetes Clusters If you’re running workloads on Kubernetes and still managing secrets manually — copying values into ConfigMaps, baking credentials into container images, or juggling base64-encoded YAML files — this guide is for you. DevOps engineers, platform teams, and cloud architects who want a cleaner, more secure way to […]
Amazon DynamoDB Throttling Deep Dive: Adaptive Capacity, Hot Keys, and Scaling
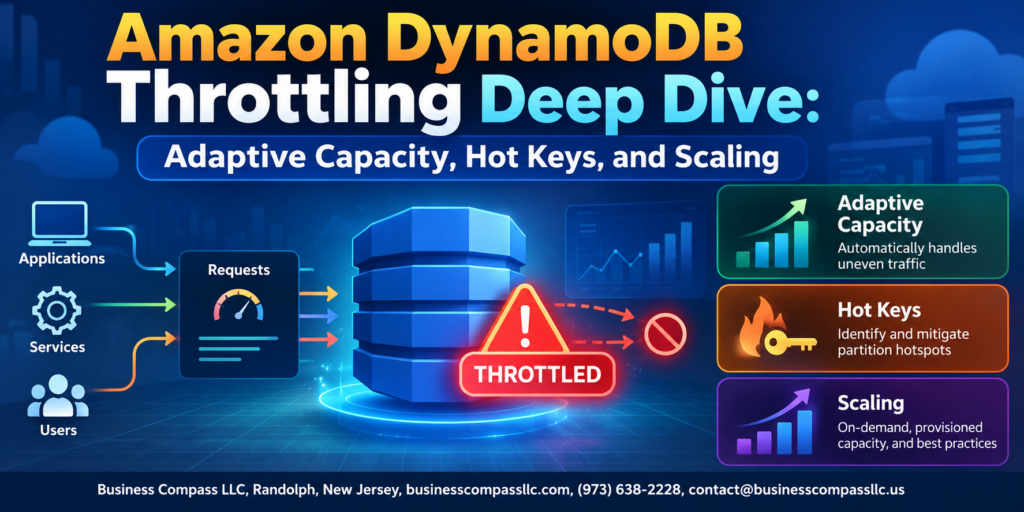
When DynamoDB Throttling Hits, Your Users Feel It First If you’ve ever watched your application slow to a crawl during a traffic spike, only to dig through logs and find a flood of ProvisionedThroughputExceededException errors, you already know how painful DynamoDB throttling can be. This guide is for backend engineers, cloud architects, and DevOps […]
AWS S3 Data Security: Find Sensitive Data with Amazon Macie
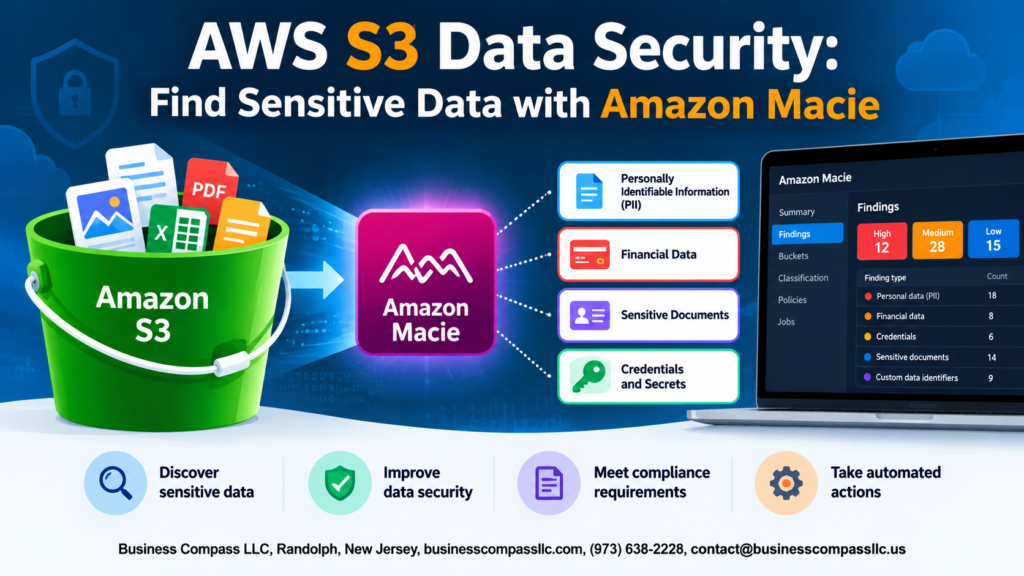
AWS S3 Data Security: Find Sensitive Data with Amazon Macie If you’re storing data in AWS S3, there’s a good chance some of it is more sensitive than you realize — think PII, credentials, or financial records sitting in buckets you haven’t audited in months. That’s a real problem, especially when compliance requirements and […]
SSH vs SSM for EC2: Ports, Keys, IAM, Logging, and Security Compared
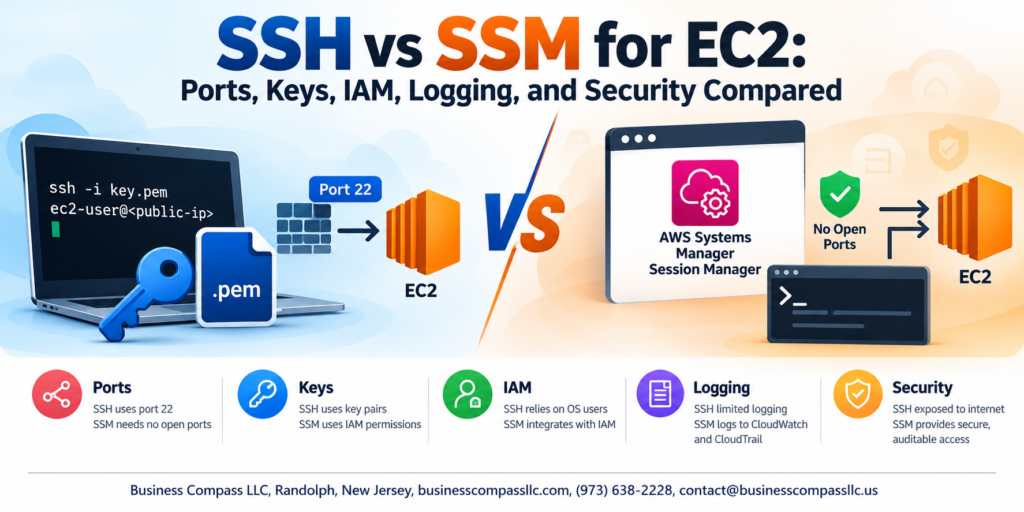
SSH vs SSM for EC2: Which One Should You Actually Be Using? If you manage EC2 instances on AWS, you’ve probably used SSH at some point. But AWS SSM Session Manager has quietly become a serious alternative — and a lot of teams don’t realize how different the two are under the hood. This […]
AWS IAM Without the Confusion: How Roles, Policies, and Permissions Really Work
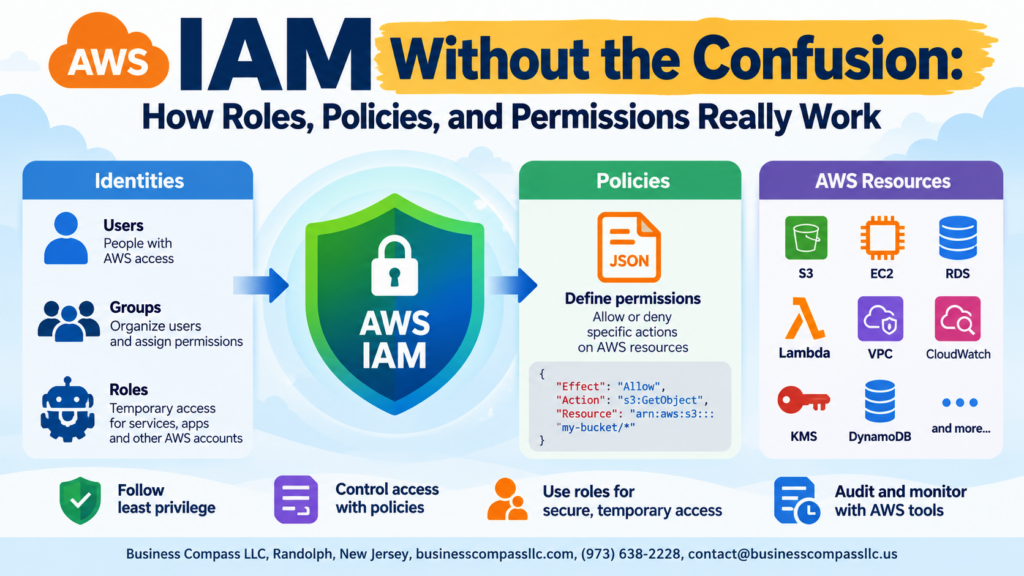
AWS IAM Without the Confusion: How Roles, Policies, and Permissions Really Work If you’ve ever stared at an AWS IAM error and had no idea why access was denied, you’re not alone. IAM — AWS Identity and Access Management — is one of those things that looks simple on the surface but gets messy […]